

Have passed EX407 exam with using your dump. Thanks.
 Adonis


Over 66059+ Satisfied Customers
Updated: Oct 12, 2026
No. of Questions: 42 Questions & Answers with Testing Engine
Download Limit: Unlimited
Instant Download: Upon successful payment, Our systems will automatically send the product you have purchased to your mailbox by email. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
PrepAwayTest has an unprecedented 99.6% first time pass rate among our customers.  We're so confident of our
products that we provide no hassle product exchange.
Free demos of every version, secure payment, instant delivery, a year of updates, and a written refund policy: PrepAwayTest makes the RedHat Red Hat Certified Specialist in Ansible Automation choice easy for 2026 EX407 candidates by making everything checkable.
| Certification Vendor: | Red Hat |
|---|---|
| Exam Name: | Red Hat Certified Specialist in Ansible Automation Exam (EX407) |
| Exam Number: | EX407 |
| Exam Duration: | 240 minutes |
| Passing Score: | 210/300 |
| Certificate Validity Period: | 3 years |
| Exam Price: | USD 400 (varies by region) |
| Exam Format: | Hands-on configuration and troubleshooting tasks, Performance-based lab exam |
| Related Certifications: | Red Hat Certified System Administrator (RHCSA) Red Hat Certified Engineer (RHCE) |
| Real Exam Qty: | Performance-based exam (number of tasks varies) |
| Available Languages: | English |
| Recommended Training: | Red Hat Ansible Automation Courses |
| Exam Registration: | Red Hat Certification Portal |
| Sample Questions: | DOWNLOAD DEMO |
| Exam Way: | Hands-on practical lab exam (onsite or remote depending on Red Hat testing provider availability) |
| Pre Condition: | Basic Linux administration skills recommended; familiarity with command line and system configuration is expected. |
| Official Syllabus URL: | https://www.redhat.com/en/services/certification |
| Section | Objectives |
|---|---|
| Playbook Development | - Playbook structure
|
| Ansible Fundamentals | - Inventory management
|
| Advanced Automation | - Security and troubleshooting
|
RedHat Red Hat Certified Specialist in Ansible Automation is an official Red Hat exam, catalogued under the code EX407. Passing it earns you the Red Hat Certified Specialist in Ansible Automation certification at the Specialist level. It also connects with Red Hat Certified System Administrator (RHCSA), Red Hat Certified Engineer (RHCE). The credential carries the vendor's authority, which is why it keeps opening doors for the people who hold it.
Yes, and for every version. PrepAwayTest provides free demos of the RedHat Red Hat Certified Specialist in Ansible Automation material so you can compare the PDF, SOFT, and online formats before deciding. After purchase, updates are free for 365 days, and when your product expires you can extend the update service at a 50% discount.
RedHat Red Hat Certified Specialist in Ansible Automation gives you Performance-based exam (number of tasks varies) questions inside 240 minutes. Rather than cramming mechanically, rehearse the pace actively: the PrepAwayTest SOFT engine teaches through timed exercises, so flagging, skipping, and returning become reflexes before exam day rather than improvisations during it.
Passing RedHat Red Hat Certified Specialist in Ansible Automation requires 210/300, and official registration costs USD 400 (varies by region). Since every retake bills the full USD 400 (varies by region) again, the sensible sequence is practice first, book second. When your PrepAwayTest practice scores clear the requirement across repeated sessions, the exam stops being a gamble.
Basic Linux administration skills recommended; familiarity with command line and system configuration is expected.
Vendor rules change over time, so confirm the current conditions before registering on the official exam page.
Registration for RedHat Red Hat Certified Specialist in Ansible Automation is handled through the official channels below.
When scheduling, note that the exam is delivered Hands-on practical lab exam (onsite or remote depending on Red Hat testing provider availability).
Red Hat recommends the following training for RedHat Red Hat Certified Specialist in Ansible Automation candidates.
Pair any training with the 42 practice questions in the PrepAwayTest EX407 package; active exercise is what makes learned material retrievable under exam pressure.
A 100% money-back guarantee covers you under stated conditions. Take the RedHat Red Hat Certified Specialist in Ansible Automation exam within 60 days of purchase; if you fail, you may claim a full refund, provided the exam matches your product. Attempts within 3 days of purchase are ineligible, as are downloaded-but-unused products, free materials, and expired orders; the candidate name must match the payer name. Submit a scanned enrollment slip and the official Score Report PDF within 2 days of the exam, and claims are processed within 7 days. You may instead exchange for two other exam products of equal value, free, keeping the update service on your original purchase.
Delivery is safe and fast: payment runs through a secure environment, files unlock for download at once, and everything is emailed to you within one minute. If nothing arrives within 2 hours, check spam and consult our online service. Installation is unlimited across your computers.
RedHat Red Hat Certified Specialist in Ansible Automation is divided into 3 official domains, led by Advanced Automation, Ansible Fundamentals, and Playbook Development. The complete breakdown is above on this page; candidates who study the syllabus first waste the least time later.
===================================================================================
control.realmX.example.com _ workstation.lab.example.com
node1.realmX.example.com _ servera.lab.example.com
node2.realmX.example.com _ serverb.lab.example.com
node3.realmX.example.com _ serverc.lab.example.com
node4.realmX.example.com _ serverd.lab.example.com
node5.realmX.example.com
- username:root, password:redhat
- username:admin, password:redhat
note1. don't change 'root' or 'admin' password.
note2. no need to create ssh-keygen for access, its pre-defined
note3. SELinux is in enforcing mode and firewalld is disabled/stop on whole managed hosts.
Create a role called apache in "/home/admin/ansible/roles" with the following
requirements:
--> The httpd package is installed, enabled on boot, and started.
--> The firewall is enabled and running with a rule to allow access to the web server.
--> template file index.html.j2 is used to create the file /var/www/html/index.html
with the output:
Welcome to HOSTNAME on IPADDRESS
--> Where HOSTNAME is the fqdn of the managed node and IPADDRESS is the IP-Address of
the managed node.
note: you have to create index.html.j2 file.
--> Create a playbook called httpd.yml that uses this role and the playbook runs on
hosts in the webservers host group.
Correct Answer:
Solution as:
----------
# pwd
/home/admin/ansible/roles/
# ansible-galaxy init apache
# vim apache/vars/main.yml
---
# vars file for apache
http_pkg: httpd
firewall_pkg: firewalld
http_srv: httpd
firewall_srv: firewalld
rule: http
webpage: /var/www/html/index.html
template: index.html.j2
:wq!
# vim apache/tasks/package.yml
---
- name: Installing packages
yum:
name:
- "{{http_pkg}}"
- "{{firewall_pkg}}"
state: latest
:wq!
# vim apache/tasks/service.yml
---
- name: start and enable http service
service:
name: "{{http_srv}}"
enabled: true
state: started
- name: start and enable firewall service
service:
name: "{{firewall_srv}}"
enabled: true
state: started
:wq!
# vim apache/tasks/firewall.yml
---
- name: Adding http service to firewall
firewalld:
service: "{{rule}}"
state: enabled
permanent: true
immediate: true
:wq!
# vim apache/tasks/webpage.yml
---
- name: creating template file
template:
src: "{{template}}"
dest: "{{webpage}}"
notify: restart_httpd
!wq
# vim apache/tasks/main.yml
# tasks file for apache
- import_tasks: package.yml
- import_tasks: service.yml
- import_tasks: firewall.yml
- import_tasks: webpage.yml
:wq!
# vim apache/templates/index.html.j2
Welcome to {{ ansible_facts.fqdn }} on {{ ansible_facts.default_ipv4.address }}
# vim apache/handlers/main.yml
---
# handlers file for apache
- name: restart_httpd
service:
name: httpd
state: restarted
:wq!
# cd ..
# pwd
/home/admin/ansible/
# vim httpd.yml
---
- name: Including apache role
hosts: webservers
pre_tasks:
- name: pretask message
debug:
msg: 'Ensure webserver configuration'
roles:
- ./roles/apache
post_tasks:
- name: Check webserver
uri:
url: "http://{{ ansible_facts.default_ipv4.address }}"
return_content: yes
status_code: 200
:wq!
# ansible-playbook httpd.yml --syntax-check
# ansible-playbook httpd.yml
# curl http://serverx
===================================================================================
control.realmX.example.com _ workstation.lab.example.com
node1.realmX.example.com _ servera.lab.example.com
node2.realmX.example.com _ serverb.lab.example.com
node3.realmX.example.com _ serverc.lab.example.com
node4.realmX.example.com _ serverd.lab.example.com
node5.realmX.example.com
- username:root, password:redhat
- username:admin, password:redhat
note1. don't change 'root' or 'admin' password.
note2. no need to create ssh-keygen for access, its pre-defined
note3. SELinux is in enforcing mode and firewalld is disabled/stop on whole managed hosts.
Install and configure Ansible on the control-node control.realmX.example.com as
follows:
-------------------------------------------------------------------------------------------
--> Install the required packages
--> Create a static inventory file called /home/admin/ansible/inventory as follows:
node1.realmX.example.com is a member of the dev host group
node2.realmX.example.com is a member of the test host group
node3.realmX.example.com & node4.realmX.example.com are members of the prod
host group
node5.realmX.example.com is a member of the balancers host group.
prod group is a member of the webservers host group
--> Create a configuration file called ansible.cfg as follows:
--> The host inventory file /home/admin/ansible/inventory is defined
--> The location of roles used in playbooks is defined as /home/admin/ansible/ roles
Correct Answer:
Solution as:
Through physical host, login to workstation.lab.example.com with user root.
# ssh [email protected]
# hostname
workstation.lab.example.com
# yum install platform-python*
# su - admin
# pwd
/home/admin/
# vim .vimrc
# mkdir -p ansible/roles
# cd ansible
# vim inventory
[dev]
servera.lab.example.com
[test]
serverb.example.com
[prod]
serverc.example.com
serverd.example.com
[balancer]
serverd.lab.example.com
[webservers:children]
prod
:!wq
# vim ansible.cfg
[defaults]
inventory = ./inventory
role_path = ./roles
remote_user = admin
ask_pass = false
[privilege_escalation]
become = true
become_method = sudo
become_user = root
become_ask_pass = false
:!wq
# ansible all --list-hosts
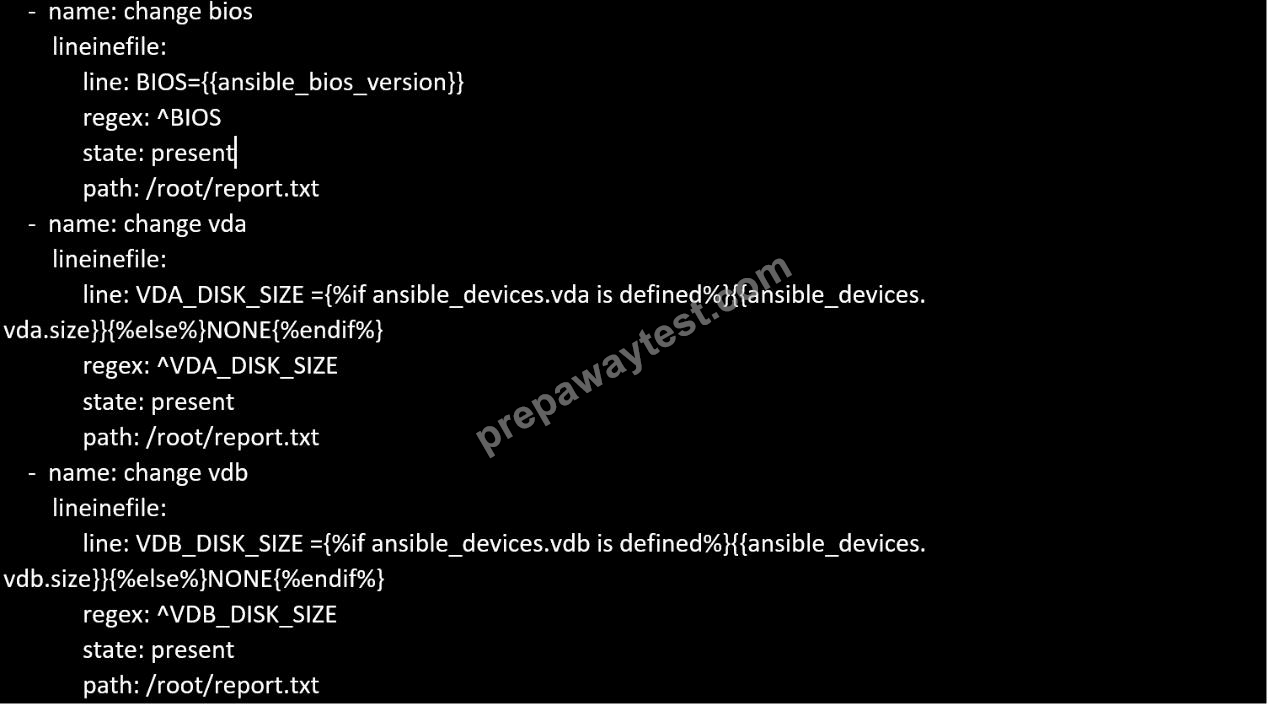
Create a file called specs.empty in home/bob/ansible on the local machine as follows:
HOST=
MEMORY=
BIOS=
VDA_DISK_SIZE=
VDB_DISK_SIZE=
Create the playbook /home/bob/ansible/specs.yml which copies specs.empty to all remote nodes' path /root/specs.txt. Using the specs.yml playbook then edit specs.txt on the remote machines to reflect the appropriate ansible facts.
Correct Answer:
Solution as: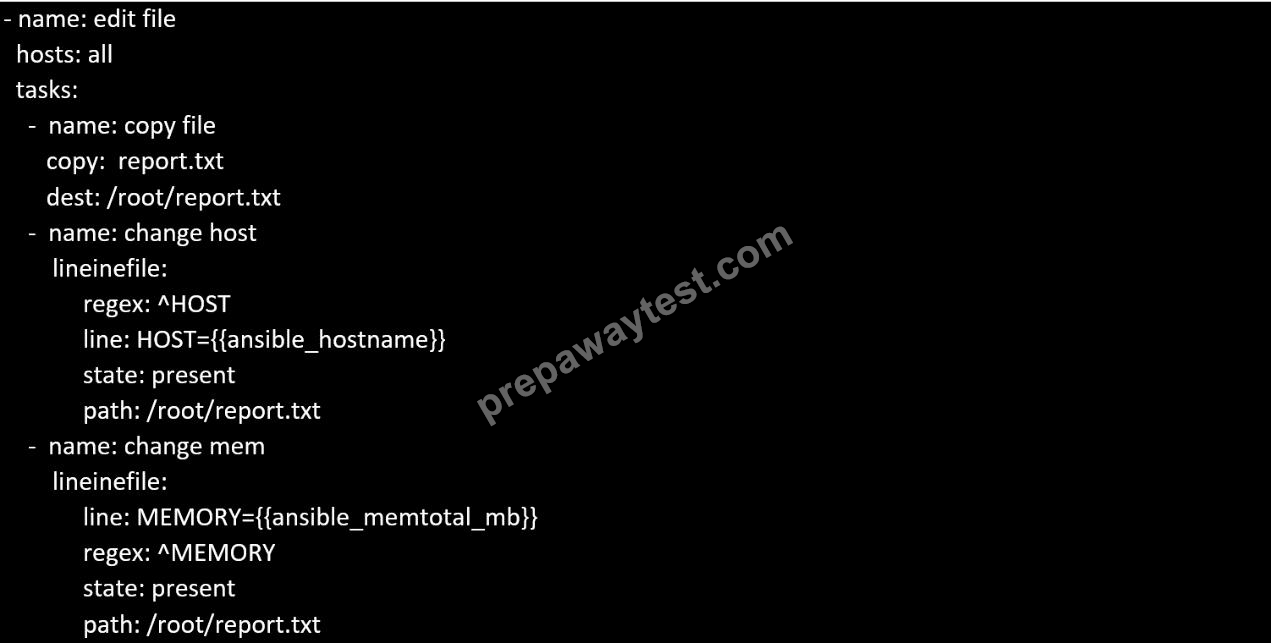
Create a file called requirements.yml in /home/sandy/ansible/roles a file called role.yml in /home/sandy/ansible/.
The haproxy-role should be used on the proxy host. And when you curl http://node3.example.com it should display "Welcome to node4.example.com" and when you curl again "Welcome to node5.example.com" The php-role should be used on the prod host.
Correct Answer:
Solution as: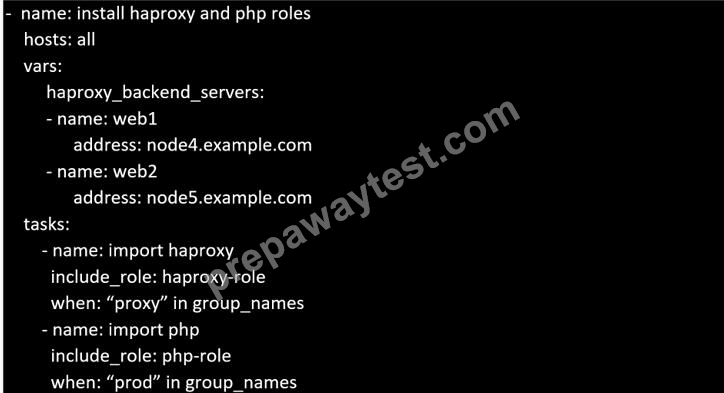
Check the proxy host by curl http://node3.example.com
Create a playbook called issue.yml in /home/sandy/ansible which changes the file /etc/issue on all managed nodes: If host is a member of (lev then write "Development" If host is a member of test then write "Test" If host is a member of prod then write "Production"
Reveal Solution Discussion 0Correct Answer:
Solution as: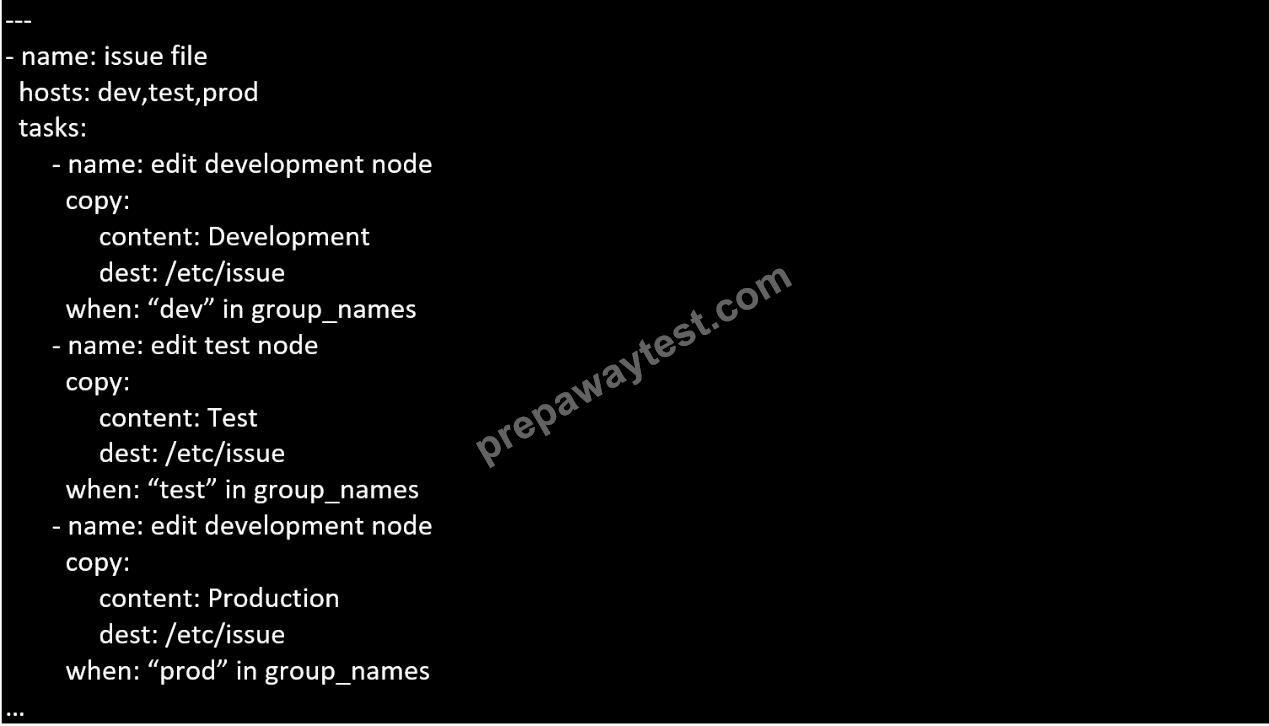
Viewing page 1 out of 9 pages.
Viewing questions 1-5 out of 42 questions.
Have passed EX407 exam with using your dump. Thanks.
Adonis
This is Oct 12, 2026, I have passed EX407 exam.
 Camille

I prepared for my EX407 exam about one week, and passed today. I have to say that EX407 dump really helped me a lot. Highly recommend!
 Lewis
When I bought EX407 exam cram, the service staff give me lots of help, thank you!
 Prima

I have to get the EX407 certification in a short time, so I used EX407 exam material to test myself ,and when I took the exam I found the questions are the one that I practiced from you.
 Beck
These EX407 exam questions are accurate, all questions and answers are correct. And they all showed up in the real exam. It is easy to pass. Guys, you can buy them!
 Quinn
The EX407 prep material was very easy, logical and well organized.
 Sophia
Your EX407 study materials are very good.
 Ingram
Today I got my EX407 certification and I am so happy about it. The easy and self-explanatory exam guide of PrepAwayTest was exceptionally helpful and effective stud High Flying Results
 Robin
I passed exam yesterday. Do not hesitate again. PrepAwayTest is reliable. The exam cram is valid
 Joy
It was the second time I tried Braindumps study guide for exam preparation. It didn't disappoint me this time also. I got through the exam easily and secured a brilliant percentage. Braindumps's study material
 Prescott
I passed my EX407 certification exam by studying from PrepAwayTest. They have very informative exam dumps and practise engines. I scored A 97%. Highly suggested
 Michell
The EX407 exam dumps are very accurate and reliable. You can rely on it. I passed my exam two days ago. Good luck!
 Vera
Trust your quality and service for the dump EX407
 Nina
I iove this EX407 exam file because i got ease access to it and the lectures were nice and elaborative. I passed the exam with confidence.
 Horace
We respect customer privacy. We use McAfee's security service to provide you with utmost security for your personal information & peace of mind.
Free update is available within 365 days after your purchase. After 365 days, you will get 50% discounts for updating.
Full refund if you fail the corresponding exam in 60 days after purchasing. And Free get any another product.
After Payment, our system will send you the products you purchase in mailbox in a minute after payment. If not received within 2 hours, please contact us.
 0
 0
 0
 0
If you have any question please leave me your email address, we will reply and send email to you in 12 hours.
Our Working Time: ( GMT 0:00-15:00 )
From Monday to Saturday
